Regulated industries face strict requirements for handling sensitive data. Healthcare organizations must comply with HIPAA, financial firms with various SEC and banking regulations, and anyone handling EU personal data with GDPR. This guide covers file sharing best practices across regulated sectors.
Common Regulatory Frameworks
Healthcare (HIPAA)
HIPAA requires specific protections for Protected Health Information (PHI):
- Encryption for data in transit and at rest
- Access controls and authentication
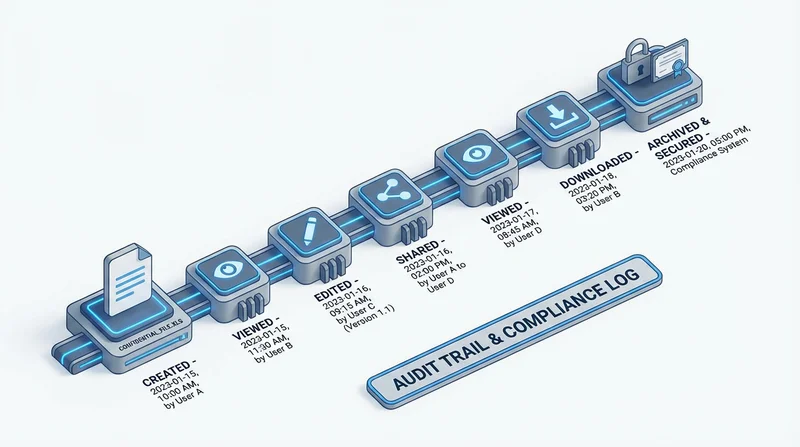
- Audit trails of all access
- Business Associate Agreements with vendors
See our complete HIPAA compliance guide.
Financial Services
Financial regulations require:
- Data protection and encryption
- Audit trails for compliance
- Access controls
- Data retention policies
See our financial services guide.
GDPR (EU Data)
GDPR requires:
- Lawful basis for processing
- Data minimization
- Security measures
- Data subject rights
- Data residency considerations
See our GDPR compliance guide.
Legal (Attorney-Client Privilege)
Legal files require:
- Strict confidentiality
- Access logging
- Secure external sharing with clients
See our legal professionals guide.
Universal Security Requirements
Regardless of specific regulations, most require:
1. Encryption
Both in transit and at rest. GetShared provides TLS 1.3 for transit and AES-256 for storage.
2. Access Controls
Limit who can access files:
3. Audit Trails
Document who accessed what and when. See audit trails guide.
4. Data Residency
Know where your data is stored. Some regulations require specific locations. See data residency guide.
Implementing Compliant File Sharing
Step 1: Classify Your Data
Understand what data you handle and what regulations apply.
Step 2: Choose Compliant Tools
Select file sharing services that meet your regulatory requirements.
Step 3: Configure Security
Enable all required security features:
- Enable 2FA (setup guide)
- Set password requirements
- Configure default expiration
- Enable audit logging
Step 4: Train Employees
Ensure staff understand requirements. See training guide.
Step 5: Monitor and Audit
Regularly review compliance:
- Check access logs
- Review active shares
- Audit security settings
GetShared for Regulated Industries
GetShared provides compliance-friendly features:
- Encryption – AES-256 at rest, TLS 1.3 in transit
- EU Data Residency – Data stored in European data centers
- Audit Logging – Complete access history
- Access Controls – Passwords, expiration, download limits
- 2FA – Strong authentication
Conclusion
Regulated file sharing requires:
- Understanding your specific requirements
- Implementing appropriate technical controls
- Training employees
- Ongoing monitoring and auditing
See also: breach prevention, security best practices.