The General Data Protection Regulation (GDPR) transformed how organizations handle personal data. File sharing – a daily activity for most businesses – must comply with these requirements. This guide explains GDPR principles and how to share files compliantly.
Understanding GDPR Basics
GDPR applies to any organization that:
- Is established in the EU, or
- Processes data of EU residents, or
- Monitors behavior of people in the EU
This means most international businesses must comply, regardless of where they're headquartered.
Key GDPR Principles for File Sharing
1. Lawful Basis
You must have a legal basis to process personal data:
- Consent
- Contract necessity
- Legal obligation
- Legitimate interests
- Public task
- Vital interests
When sharing files containing personal data, document your lawful basis.
2. Purpose Limitation
Personal data should only be used for specified, explicit purposes. Don't share files containing personal data for purposes beyond what individuals were told.
3. Data Minimization
Share only what's necessary. Instead of sharing an entire database, extract only required records.
4. Accuracy
Shared data should be accurate and up-to-date. Use file versioning to ensure recipients have current information.
5. Storage Limitation
Don't keep personal data longer than necessary. link expiration helps automate this compliance requirement.
6. Security
Article 32 requires "appropriate technical and organizational measures" including encryption. GetShared's end-to-end encryption is specifically mentioned as a recommended safeguard.
Technical Measures for GDPR Compliance
Encryption
GDPR Article 32 explicitly recommends encryption. GetShared implements:
- end-to-end encryption (data encrypted before upload)
- TLS 1.3 for data in transit
- AES-256 encryption (same as banking)
With E2EE, even if data is intercepted, it's unreadable without keys.
Access Controls
Implement controls ensuring only authorized personnel access personal data:
- password-protected sharing for external shares
- two-factor authentication for accounts
- Granular permissions (team collaboration features)
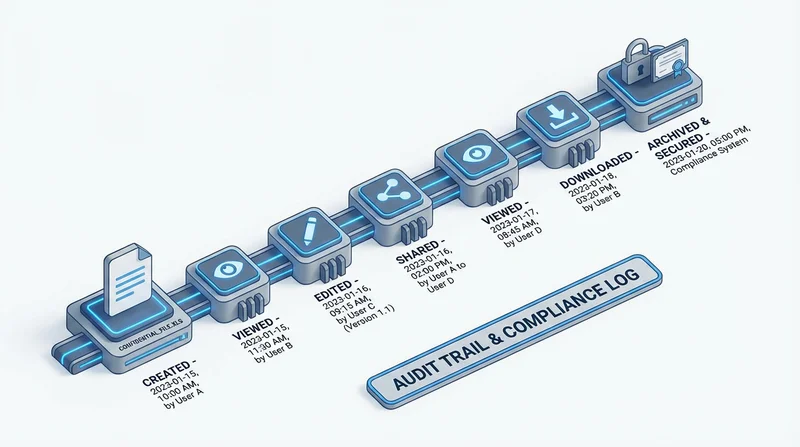
- Access logging and audit trails
Data Portability
GDPR grants individuals the right to receive their data in machine-readable format. Cloud storage inherently supports this – data can be exported easily.
Organizational Measures
Data Processing Agreements
When using cloud services for personal data, you need Data Processing Agreements (DPAs). GetShared provides DPAs for business accounts covering:
- Purpose and duration of processing
- Types of personal data processed
- Sub-processor disclosures
- Security measures
- Breach notification procedures
Staff Training
Ensure employees understand:
- What constitutes personal data
- Secure sharing procedures
- When to use additional protection
- Breach reporting requirements
Our security best practices guide provides training foundations.
Breach Response Plan
GDPR requires breach notification within 72 hours. Prepare by:
- Documenting incident response procedures
- Using download tracking to detect unauthorized access
- Maintaining ability to revoke access quickly
- Keeping contact information for Data Protection Authority
Sharing Personal Data with Third Parties
Within the EU/EEA
Sharing within European Economic Area is generally permitted with appropriate safeguards. Use GetShared's security features for protection.
Outside the EU/EEA
Transfers to third countries require additional protections:
- Adequacy decisions (UK, Switzerland, etc.)
- Standard Contractual Clauses
- Binding Corporate Rules
GetShared's EU data residency option keeps data within Europe for organizations requiring it.
Practical GDPR-Compliant Sharing Workflow
Before Sharing
- Verify lawful basis for sharing
- Minimize data to what's necessary
- Ensure data is accurate
- Confirm recipient has need-to-know
When Sharing
- Use encrypted platform (GetShared)
- Enable password-protected sharing
- Set link expiration appropriate to purpose
- Enable download tracking
- Share password through separate channel
After Sharing
- Document the share in your records
- Monitor downloads for anomalies
- Revoke access when no longer needed
- Retain logs for compliance
Subject Access Requests
Individuals can request copies of their data. Cloud storage helps by:
- Centralizing data in searchable location
- Enabling easy export
- Maintaining access logs showing data locations
Right to Erasure
Individuals can request deletion of their data. GetShared supports this:
- Permanently delete files containing personal data
- Version history is also deleted
- Shared links are immediately invalidated
Documentation and Accountability
GDPR requires demonstrating compliance. Maintain records of:
- Processing activities
- Security measures implemented
- Data sharing instances
- Training conducted
- Incident response actions
GetShared's GDPR Features
| GDPR Requirement | GetShared Feature |
|---|---|
| Encryption (Art. 32) | End-to-end encryption |
| Access Control (Art. 32) | Password protection, 2FA, permissions |
| Storage Limitation (Art. 5) | Link expiration |
| Accountability (Art. 5) | Audit logs, download tracking |
| Data Portability (Art. 20) | Easy export functionality |
| Erasure (Art. 17) | Permanent deletion |
Conclusion
GDPR compliance in file sharing requires both technical measures and organizational practices. GetShared provides the technical foundation with encryption, access controls, and audit capabilities. Combined with appropriate policies and training, you can share files confidently while meeting regulatory requirements.
Ready for GDPR-compliant file sharing? sign up for GetShared and implement proper data protection from day one.